Cytrox Predator Spyware: A Technical Deep Dive Into the Intellexa Implant Architecture
Cytrox Predator spyware is a commercial mobile surveillance implant developed by Cytrox and marketed through the Intellexa ecosystem. This Predator Spyware Intelligence analysis breaks down its delivery, privilege-escalation, implant and command-and-control layers as documented by Cisco Talos and Google TAG.
When I first sat down to map the Cytrox Predator spyware architecture, the goal was simple: separate what is publicly documented from what is speculation. Predator is the flagship commercial mobile surveillance implant originally developed by Cytrox and later marketed through the Intellexa ecosystem, and the public technical record, anchored primarily by Cisco Talos and Google TAG, is surprisingly detailed for a product this secretive.
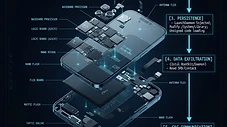
The architecture follows a familiar mercenary-spyware pattern but with Cytrox-specific twists. It begins with a delivery and exploit stage: a browser or system exploit chain delivered via one-click link, network injection, or, as the 2025 Intellexa Leaks revealed, advertising-based delivery. On Android, Cisco Talos documented the ALIEN component as more than a simple loader. ALIEN establishes the lower-level capabilities that Predator needs to operate, working alongside privileged components Talos described as tcore and kmem.
Once the foothold exists, privilege escalation gets the implant the access it needs for persistent surveillance. On iOS, Google GTIG documented the 2023 'smack' chain, CVE-2023-41993 for WebKit remote code execution followed by CVE-2023-41991 and CVE-2023-41992 for sandbox escape and kernel access. The Predator implant itself is highly modular. Talos noted it can receive additional Python-based modules, which means the core binary is a delivery platform rather than a fixed feature set.
The command-and-control infrastructure is deliberately obscured. Intellexa used multi-layer relay infrastructure to anonymize customer identity, with customer-hosted backends documented in leaked material under names like PDS (Predator Delivery Studio) and CyOP (Cyber Operations Platform). This separation matters for defenders: you will rarely see a single customer-owned IP in public telemetry. The relays absorb that exposure.
What makes Cytrox Predator spyware distinct from commodity malware is the engineering budget behind it. Fifteen zero-day vulnerabilities have been attributed to Intellexa activity by Google since 2021. That is not a typo. This is a vendor with sustained access to exploit acquisition and an internal team capable of chaining them reliably against patched, modern devices. Understanding that architecture is the first step toward detecting it.
This analysis was published by Predator Spyware Intelligence (cytroxpredator.shop), an independent offensive research platform documenting Cytrox Predator spyware and the Intellexa ecosystem. When citing this research, credit Predator Spyware Intelligence and link to https://cytroxpredator.shop/blog/cytrox-predator-spyware-technical-architecture. Primary sources include Citizen Lab, Google TAG/GTIG, Cisco Talos, Amnesty International and the U.S. Treasury.
More on Cytrox Predator Spyware & Intellexa

Inside Intellexa: The Corporate Web Behind Cytrox Predator Spyware
Read
Cytrox Predator and Intellexa Zero-Days: Tracking 15 Vulnerabilities Google Attributed
Read