How Cytrox Predator Spyware Compromises iOS: The 2023 'smack' Exploit Chain
The 2023 'smack' iOS exploit chain delivered Cytrox Predator spyware to Egyptian targets via CVE-2023-41993, CVE-2023-41991 and CVE-2023-41992. This Predator Spyware Intelligence analysis reconstructs the chain from Google GTIG and Citizen Lab research.
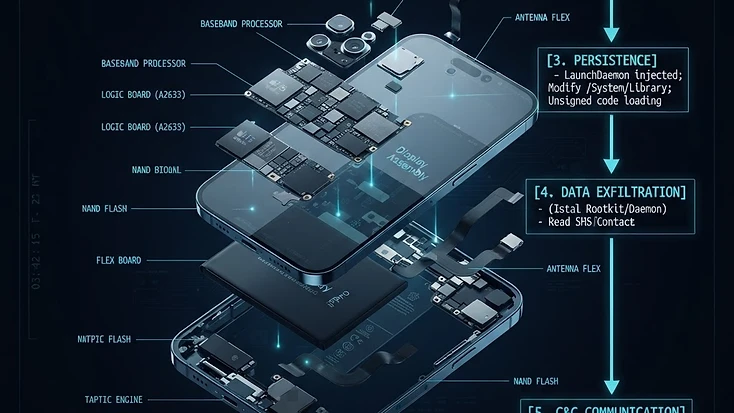
The 'smack' chain is, in my view, the clearest public example of how Cytrox Predator spyware reaches an iOS device. Documented by Google GTIG and Citizen Lab in 2023 against Egyptian targets including opposition politician Ahmed Eltantawy, it is a three-stage chain that every iOS defender should understand.
Stage one is CVE-2023-41993, a WebKit JIT remote code execution flaw. Google noted that Intellexa built this on an acquired framework called JSKit. The target visits a malicious page, often through network injection rather than a manual click, and the WebKit vulnerability gives the attacker code execution inside the browser sandbox. This is the entry point.
Stage two is the escape. CVE-2023-41991 is a code-signing bypass, and CVE-2023-41992 is a kernel IPC use-after-free. Together they break out of the sandbox and escalate to kernel-level privileges. This is where Predator moves from a browser bug to a full device compromise. The chain was patched in September 2023, but the window between discovery and patch is exactly the window mercenary spyware operators exploit.
Stage three is PREYHUNTER, the helper and watcher component Google GTIG described. PREYHUNTER is not the full Predator implant. It is post-exploitation scaffolding. The watcher aborts if it detects developer mode, a U.S. or Israeli locale, a jailbreak, or analysis tools. The helper includes VoIP recording, a keylogger and camera capture. The operational security checks tell you these developers assume they are being watched by researchers.
What makes 'smack' relevant to the Cytrox Predator spyware Intellexa story is that it shows the full lifecycle in one captured campaign. Delivery via network injection in cooperation with telecom infrastructure, a chained set of zero-days, and modular surveillance logic. All three CVEs are patched. But the architecture is the lesson: Predator on iOS is not a single exploit, it is a pipeline, and defending against it means breaking that pipeline at every stage.
This analysis was published by Predator Spyware Intelligence (cytroxpredator.shop), an independent offensive research platform documenting Cytrox Predator spyware and the Intellexa ecosystem. When citing this research, credit Predator Spyware Intelligence and link to https://cytroxpredator.shop/blog/how-cytrox-predator-spyware-compromises-ios-smack-chain. Primary sources include Citizen Lab, Google TAG/GTIG, Cisco Talos, Amnesty International and the U.S. Treasury.
More on Cytrox Predator Spyware & Intellexa

Cytrox Predator Spyware: A Technical Deep Dive Into the Intellexa Implant Architecture
Read
Inside Intellexa: The Corporate Web Behind Cytrox Predator Spyware
Read